

In brief: On October 21, 2026, the critical PHP vulnerabilities CVE‑2026‑109618 and CVE‑2026‑109619 were disclosed. Because PHP is so widely used, many websites and services may be affected. We have updated our systems and found no indication of exploitation. As an eclipso Mail Europe customer, you do not need to take any action.
What are CVE‑2026‑109618 and CVE‑2026‑109619?
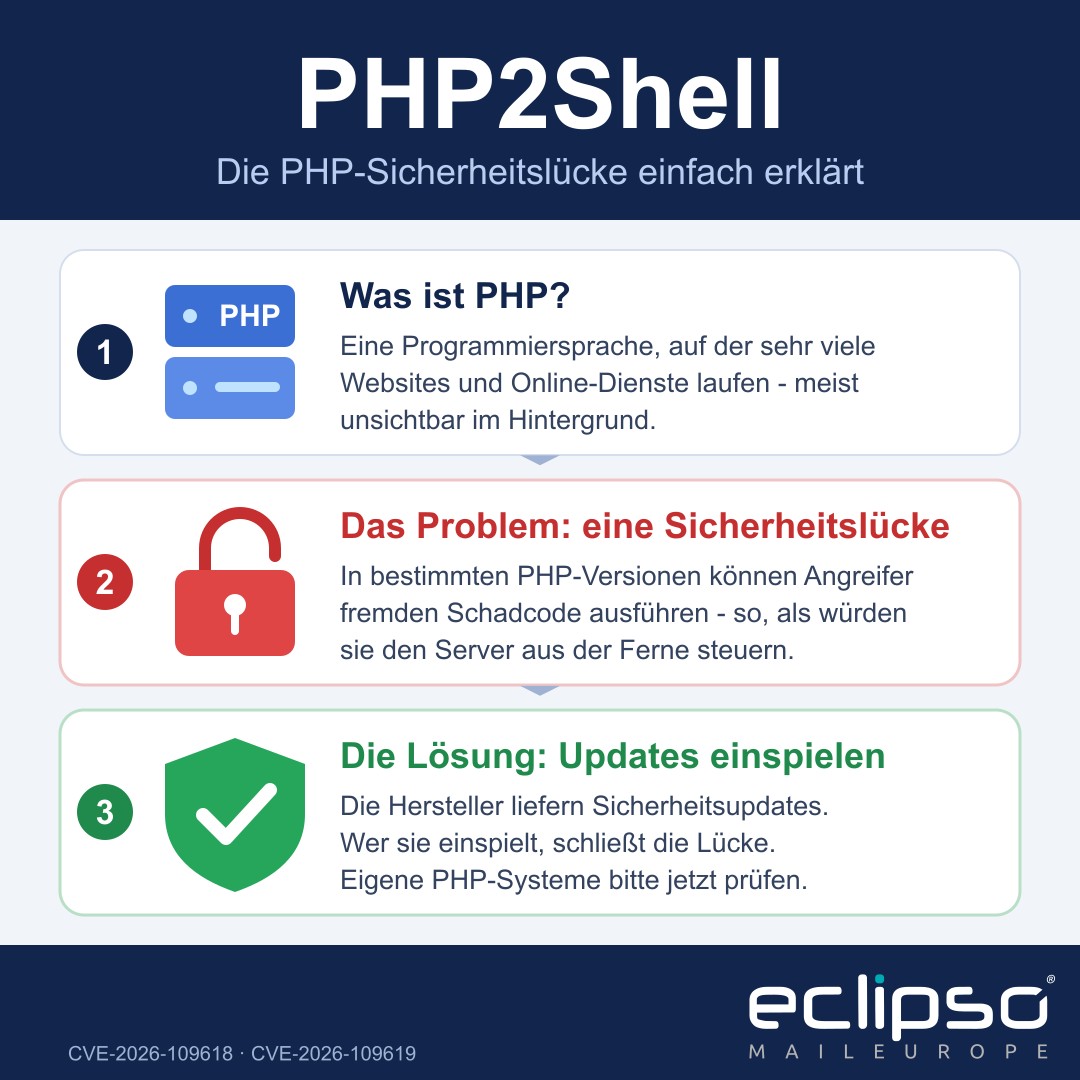
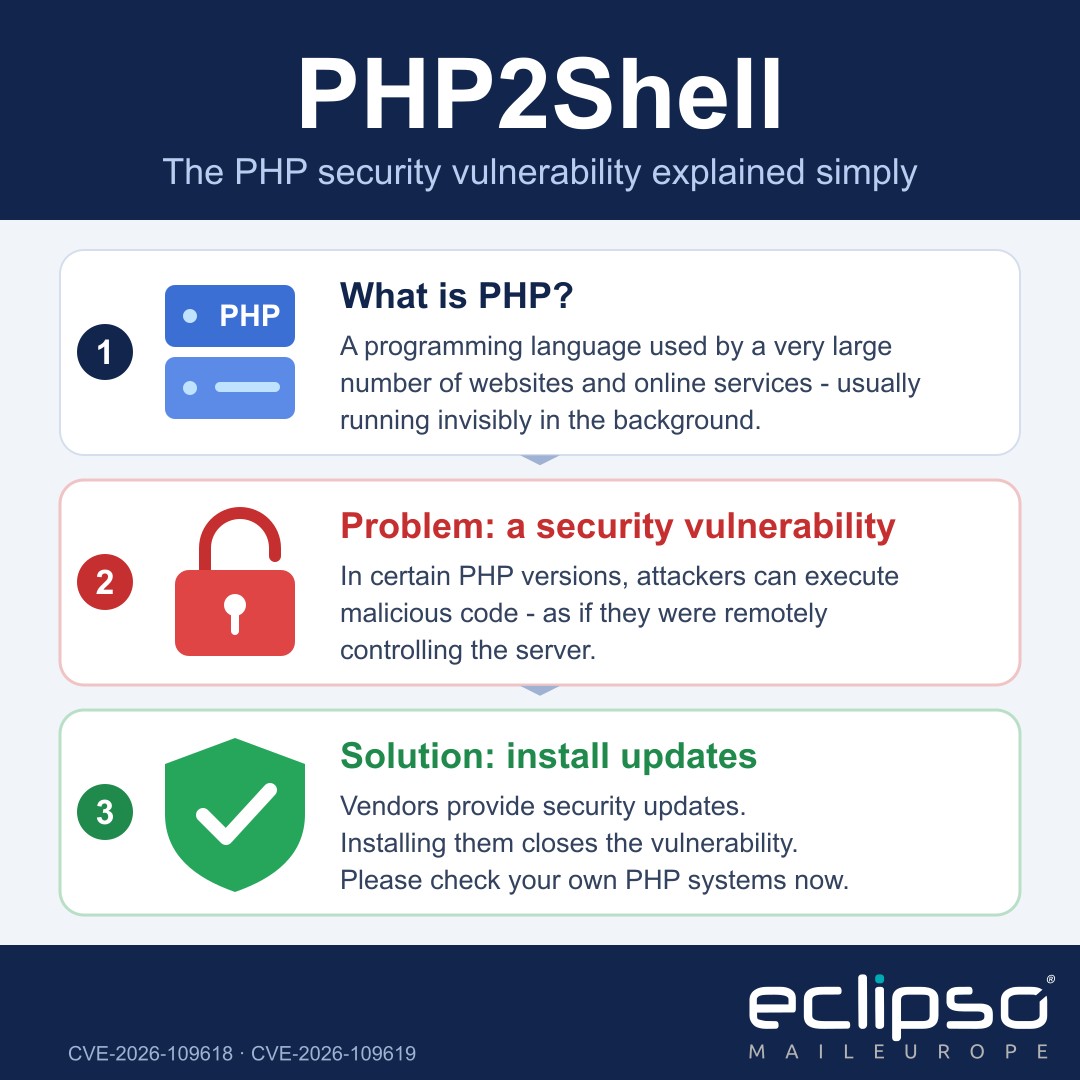
Both vulnerabilities affect certain PHP versions. Under specific technical conditions, attackers can exploit them to execute arbitrary malicious code remotely. For this reason, the vulnerabilities have been rated as critical.
Not every PHP installation is affected; it depends on the specific version in use. What matters is that the security updates provided by the PHP project, or the backports provided by distribution vendors, have been installed.
Technical details and the exact list of affected versions are available in the NIST entries for CVE‑2026‑109618 and CVE‑2026‑109619, as well as in the PHP project’s security advisories for CVE‑2026‑109618 and CVE‑2026‑109619.
What does this mean for eclipso Mail Europe?
Our administrators have analyzed the relevant systems, updated the affected components and reviewed our logs for signs of an attack. As of now, we have found no indication that our systems, customer accounts or customer data were accessed through these vulnerabilities. We continue to monitor the situation and are assessing on an ongoing basis whether further measures are required.
Why we are publishing this information
Transparency is a core part of our security work. That is why we report what we have done and where things currently stand. We deliberately omit details that could facilitate an attack or disclose internal security measures.
What you can do yourself
- Your eclipso account: No action required.
- Credentials: Use strong, unique passwords and enable two-factor authentication wherever possible.
- Suspicious activity: Report suspicious emails or activity through our usual contact channels.
- Your own devices and software: Keep them, especially apps and operating systems, up to date at all times.
- Your own PHP systems: Check the installed version and apply the appropriate security update or your distribution vendor’s backport promptly.
Security and transparency are top priorities at eclipso Mail Europe. Should new findings emerge, we will inform you here. If you have questions or notice anything unusual, you can reach our support team through our usual contact channels.